The complete IT service management platform — 100 % in your own infrastructure.
From tickets and incidents through assets to workflows and a continuously traceable audit history — for organizations that take data sovereignty, GDPR and NIS2 seriously.
The Problem
Tickets in one tool, hardware in Excel, approvals via email, audit evidence nowhere. Four systems, four versions of the truth — and no thread to follow in an audit.
- ✕Fragmented ticket systems
- ✕Excel-based asset lists
- ✕Manual approvals via email
- ✕No traceability
- ✕Growing compliance demands
- ✕No central overview
- ✓Service, assets & workflows in one system
- ✓Hardware lifecycle instead of Excel
- ✓Automated approvals with substitution
- ✓Continuously traceable audit history
- ✓Role model & visibility scoping
- ✓One central overview
Why Organizations Choose Eviworx
Your data stays in your infrastructure. No SaaS dependency, no storage in third-party clouds.
A cryptographically (SHA-256) chained audit history makes changes continuously traceable and supports audit and compliance processes.
Visual workflows automate approvals, escalations and recurring standard processes.
Container-native architecture — deployment in your own environment, without external dependencies.
What You Cover with Eviworx
Four areas instead of fifty individual features.
Plus: reporting & analytics, eLibrary, integrations and substitution rules — 50+ modules in a single platform.
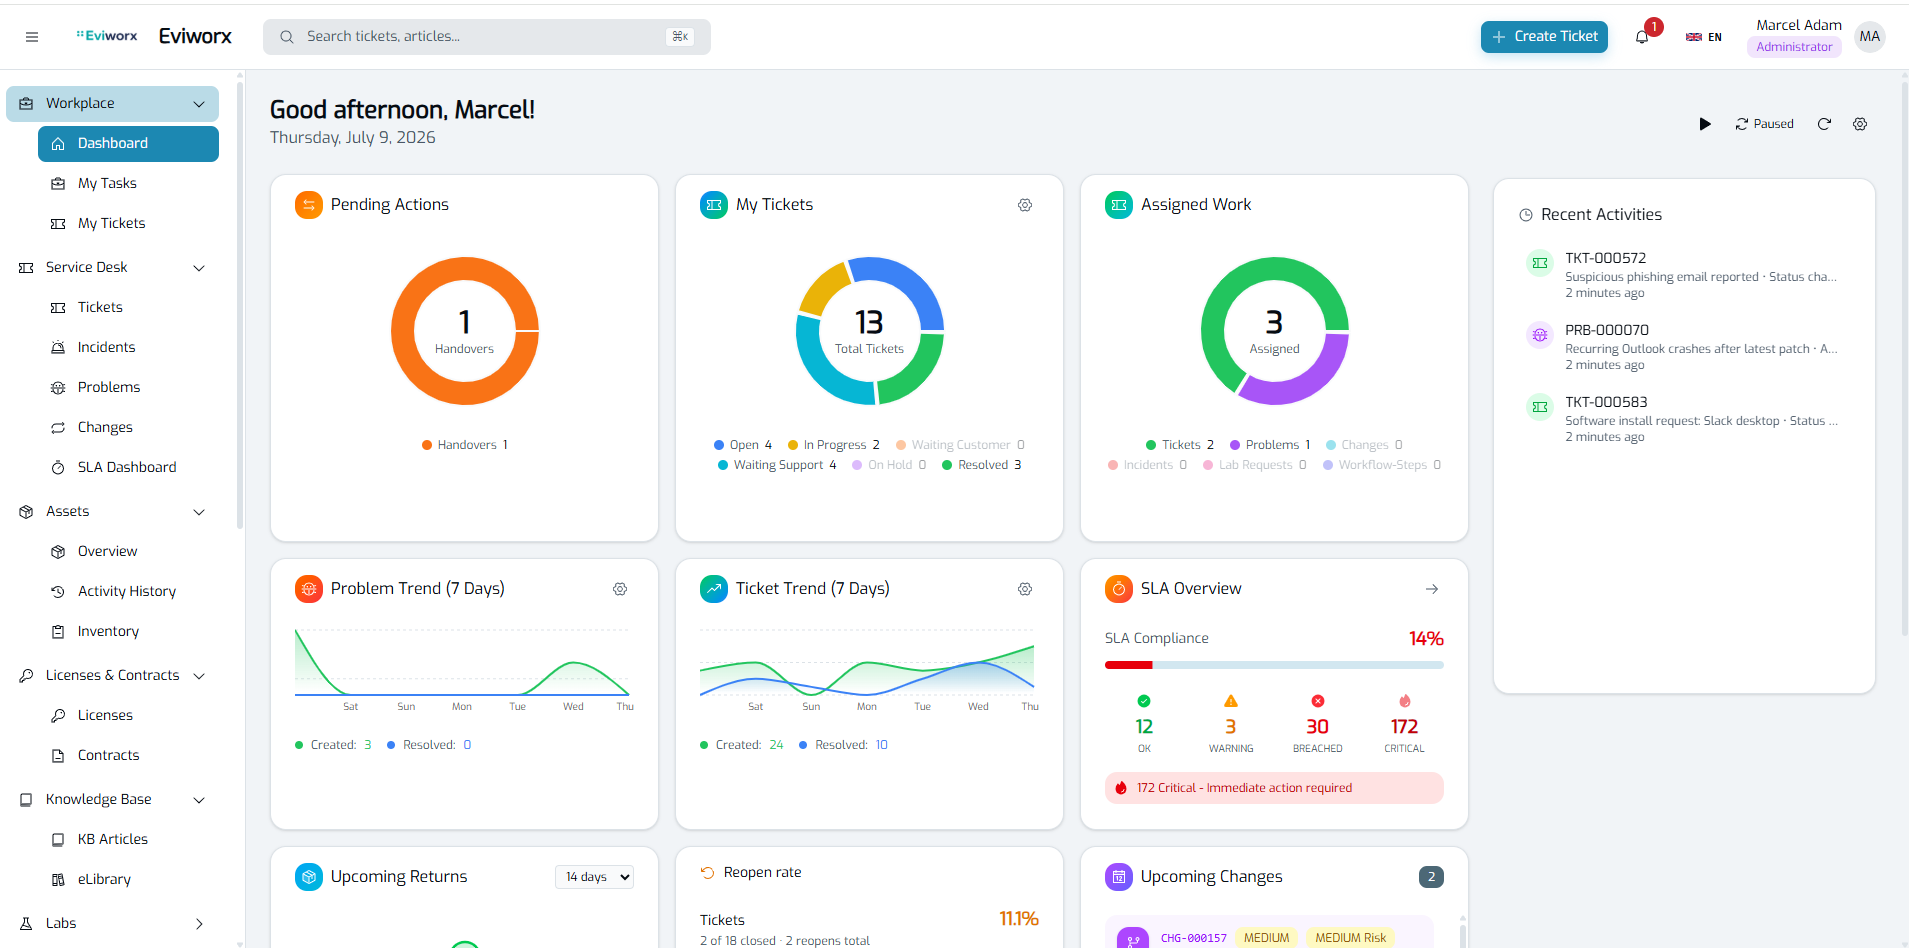
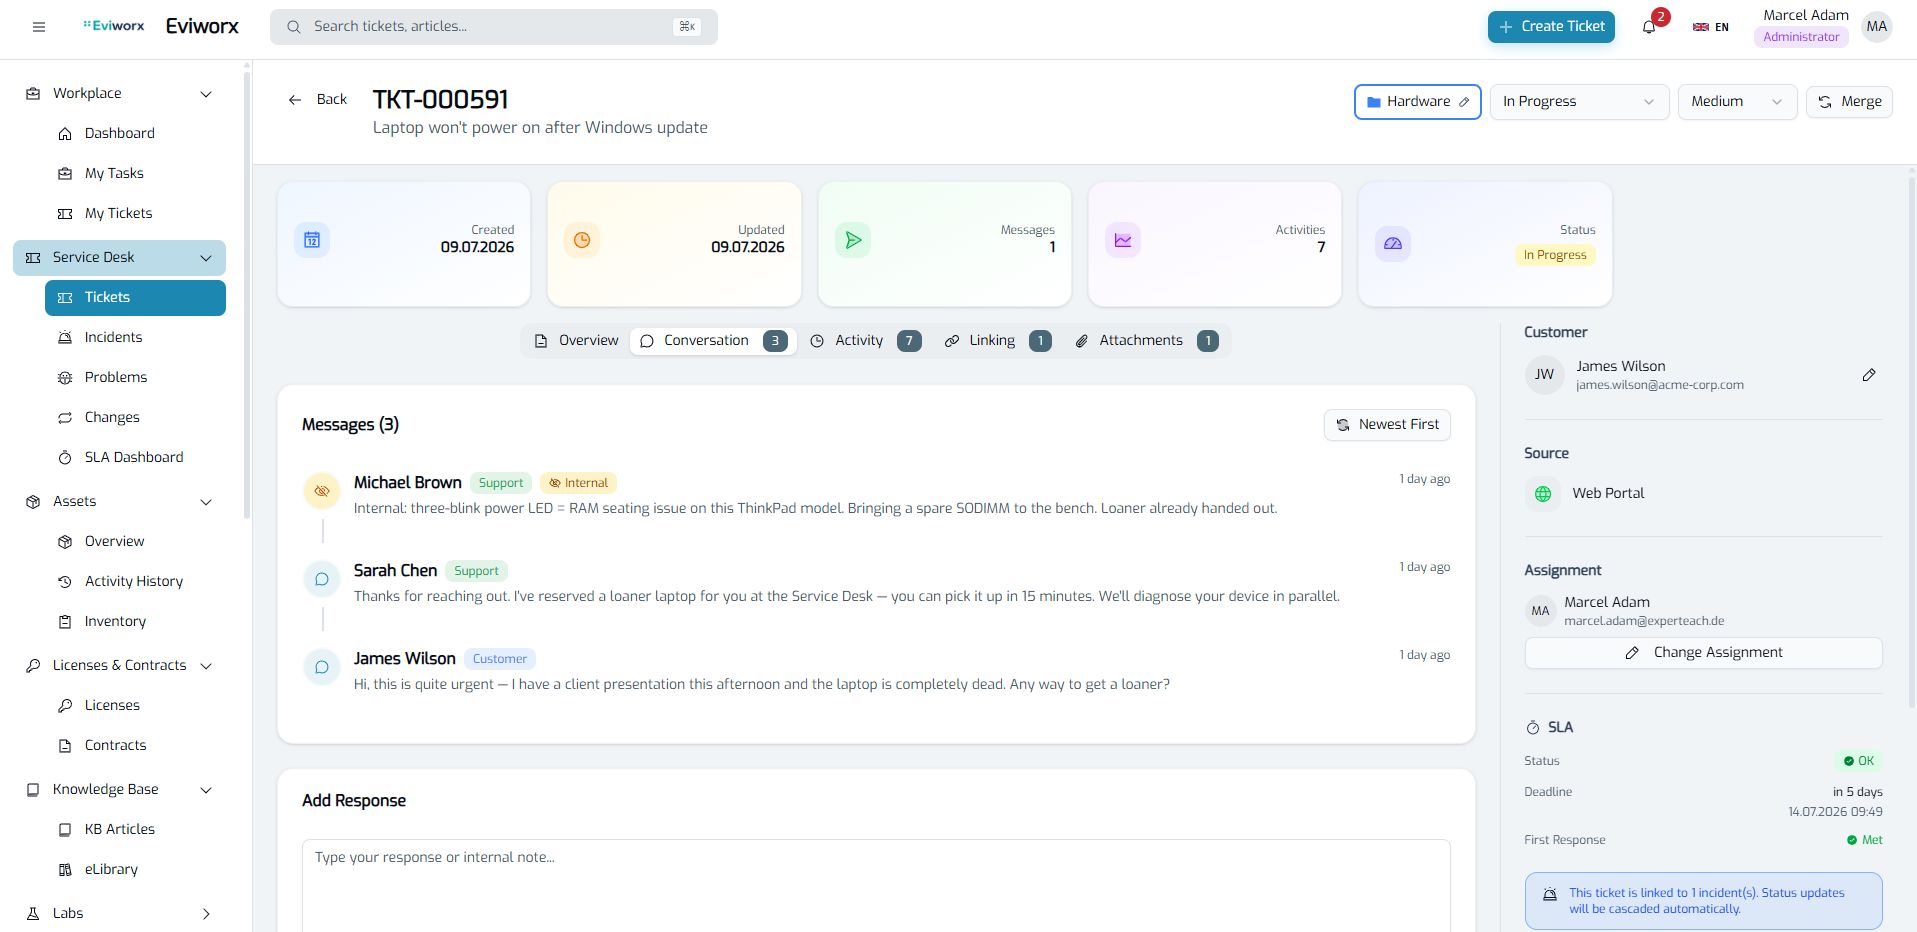
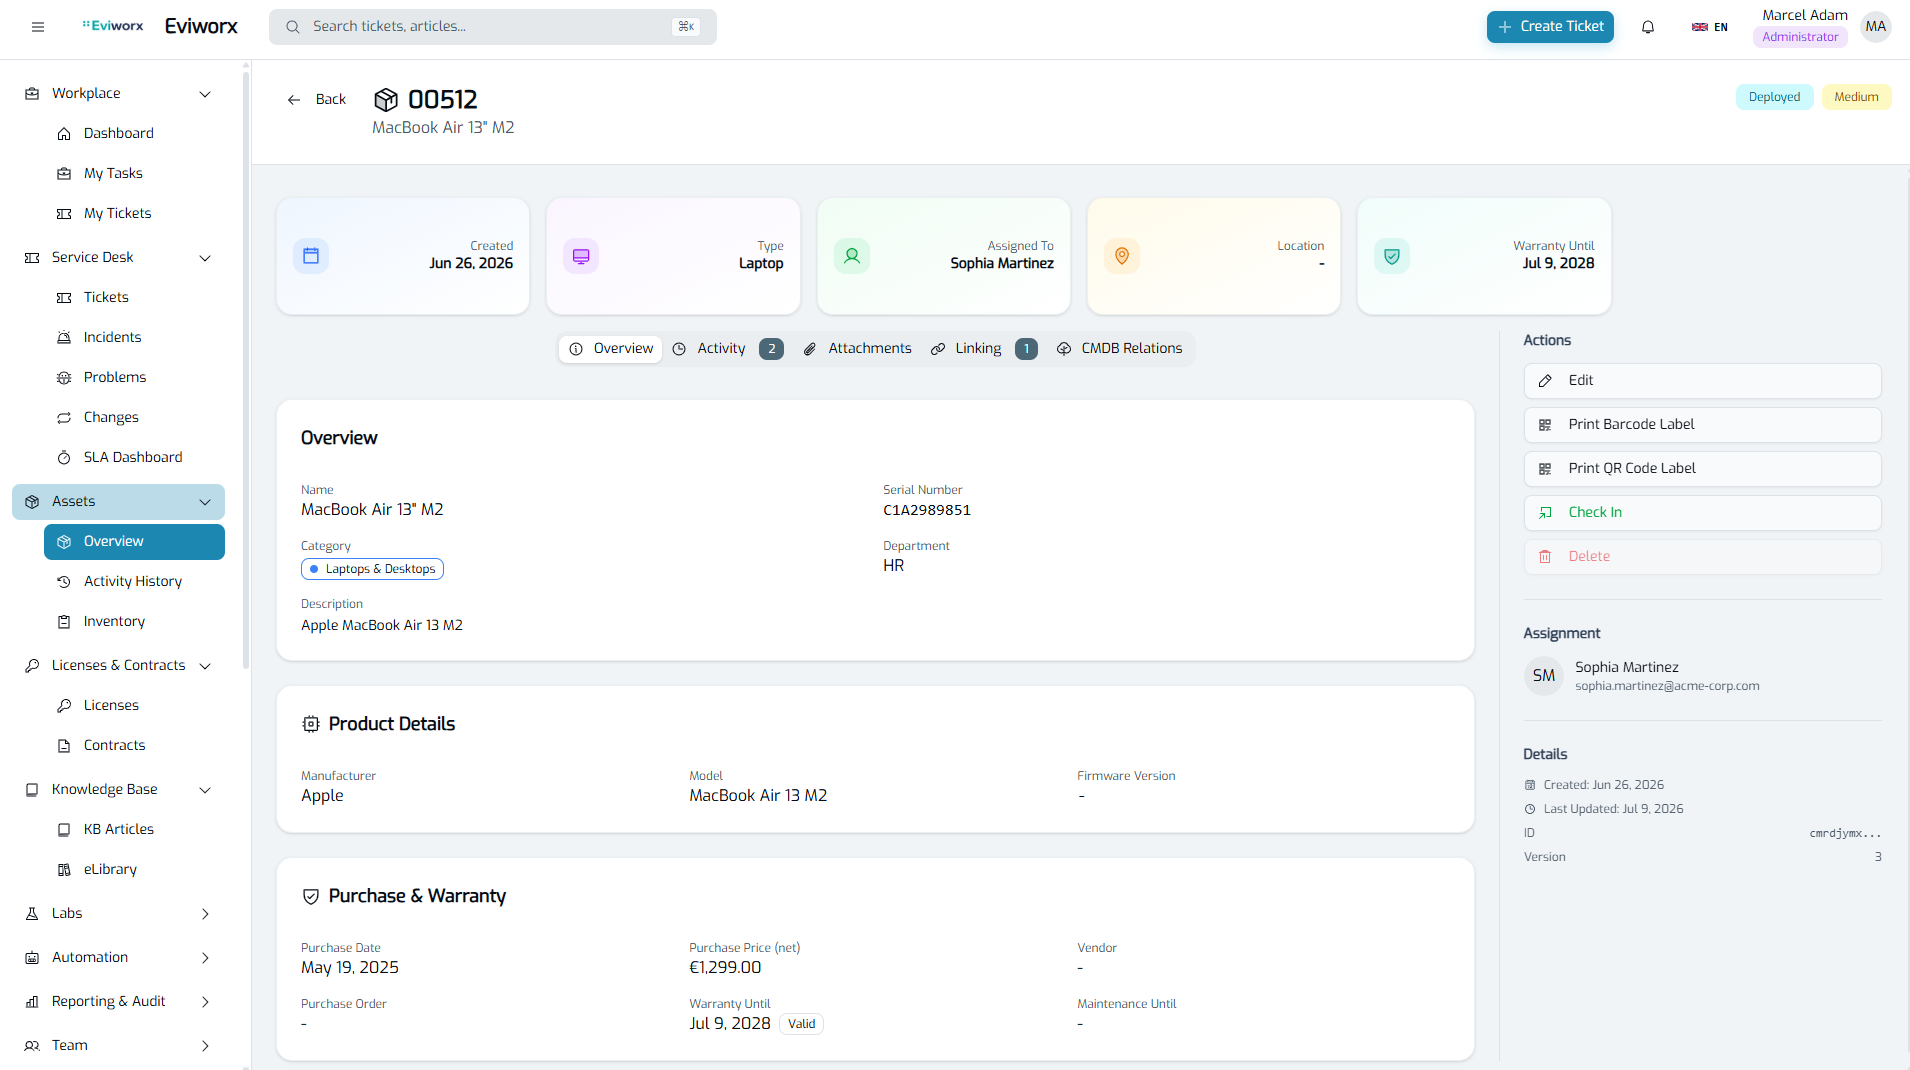
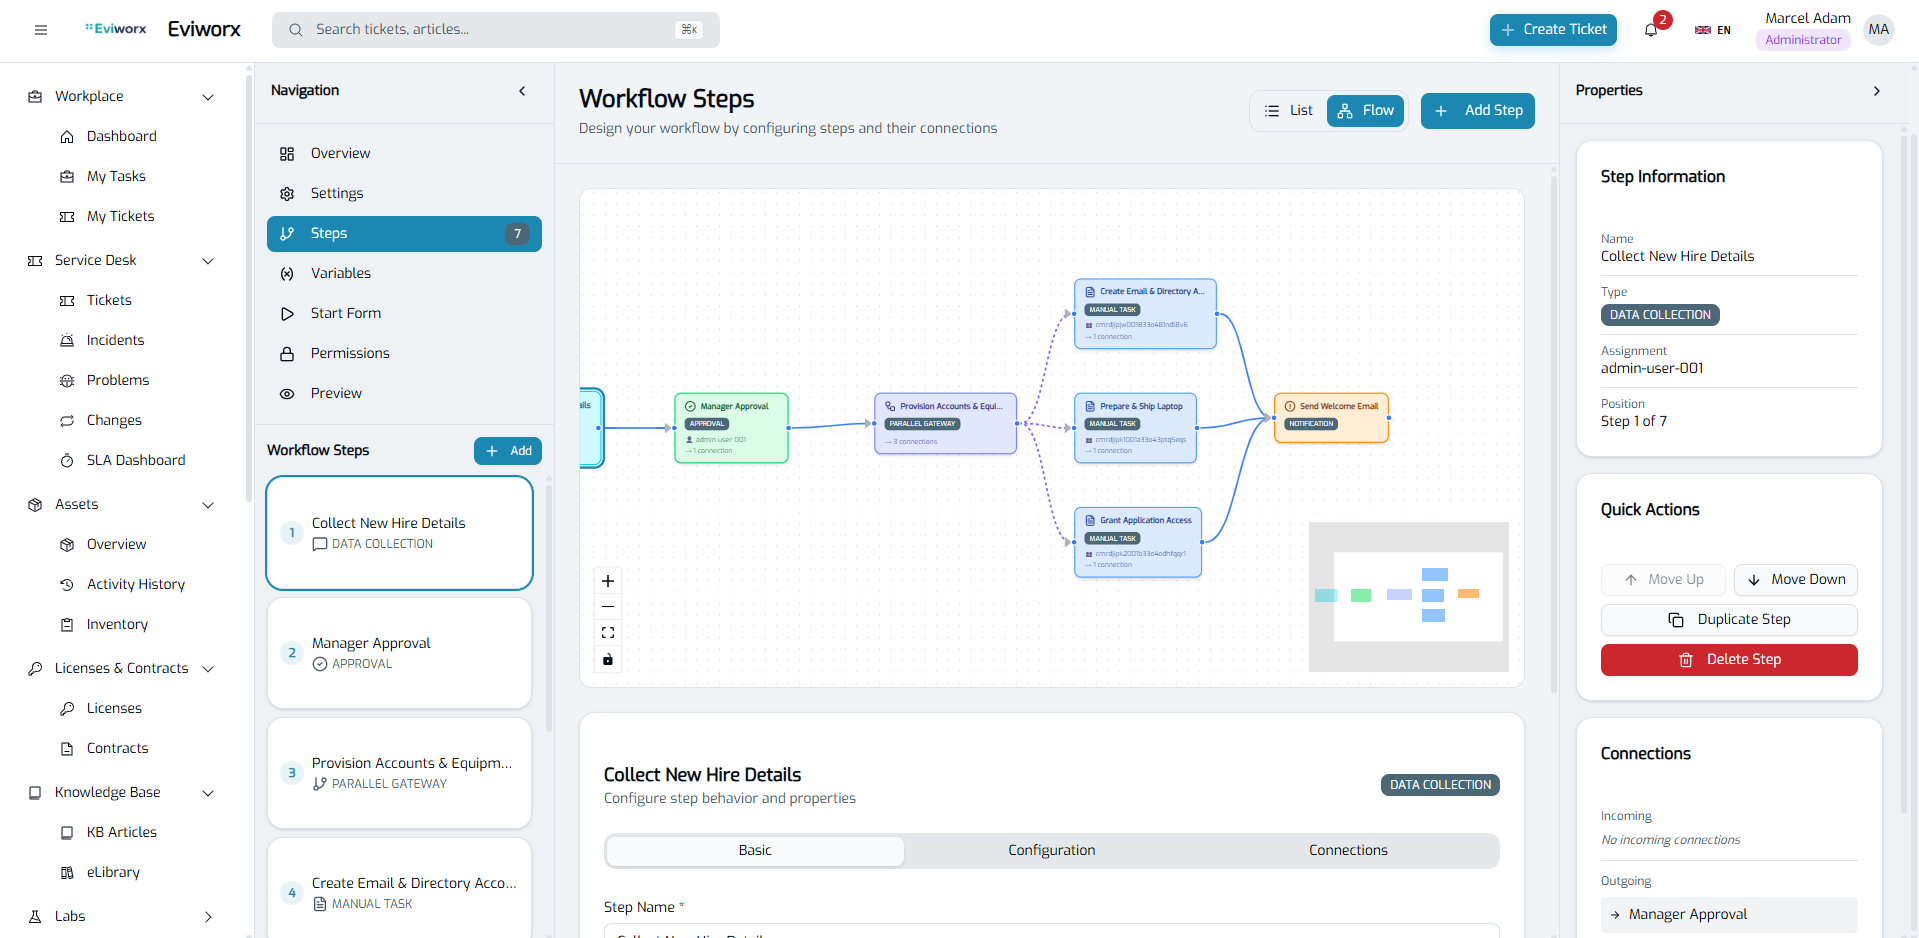
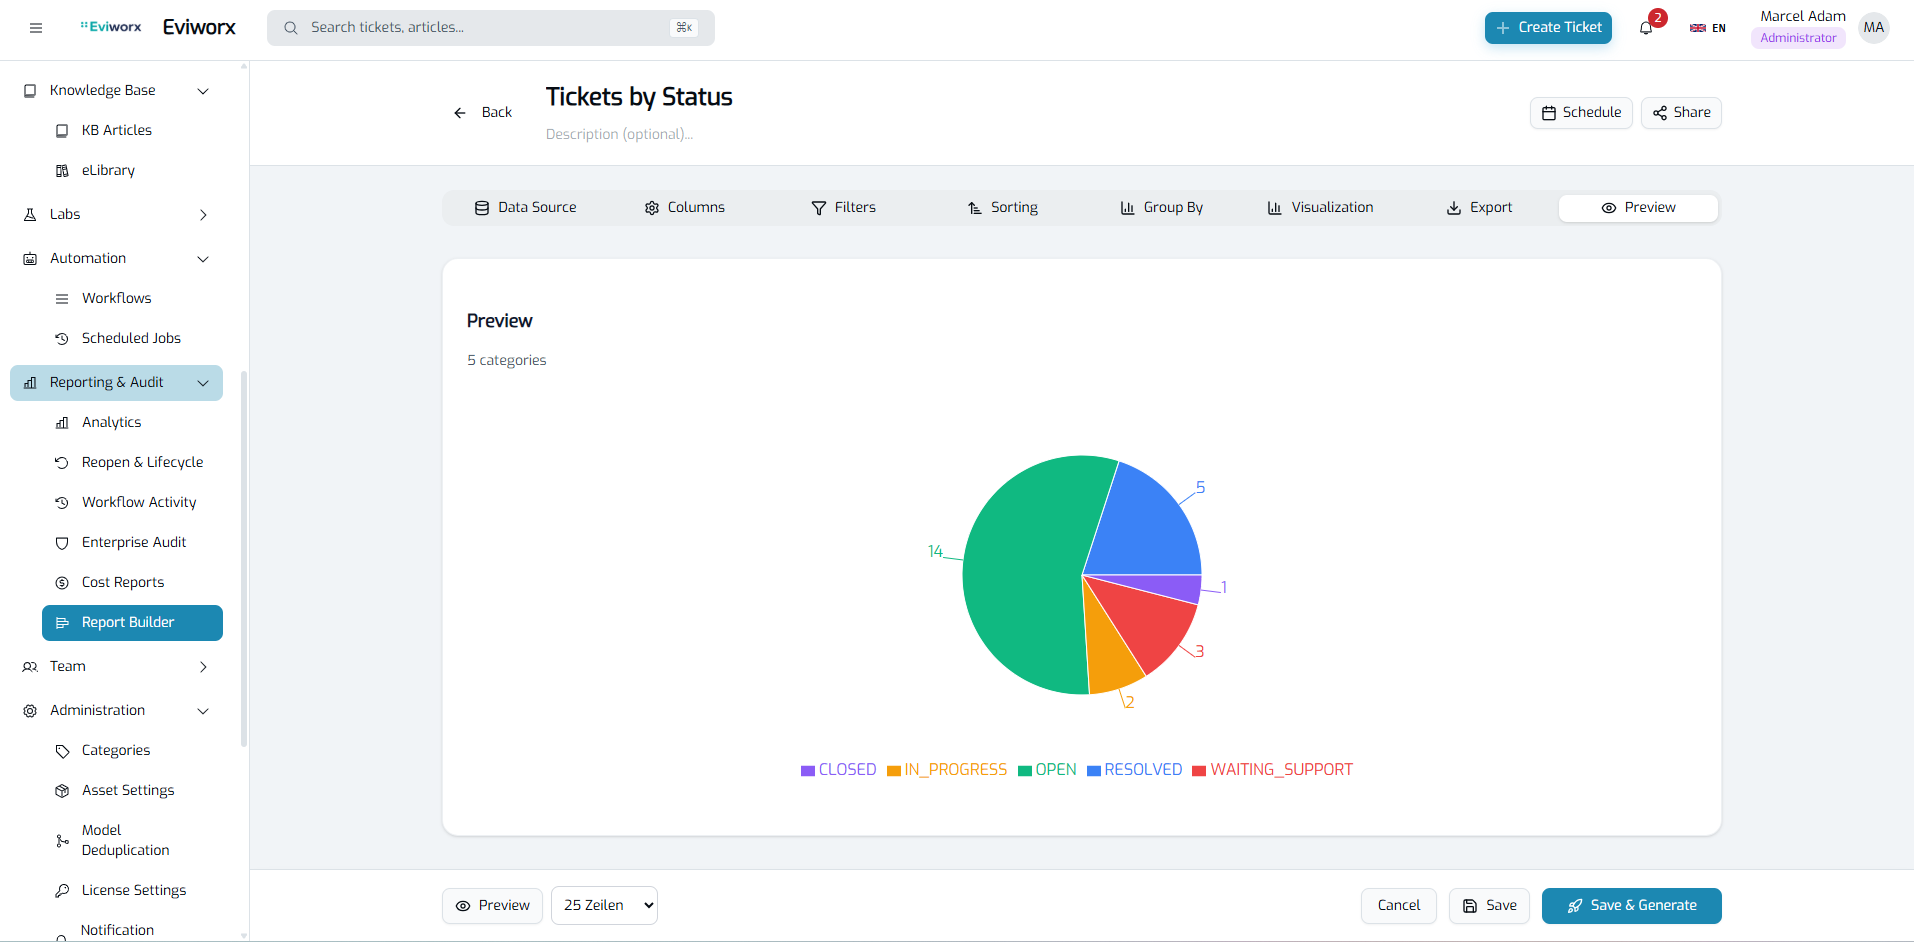
A Look Inside the Product
One interface for your entire IT operation.
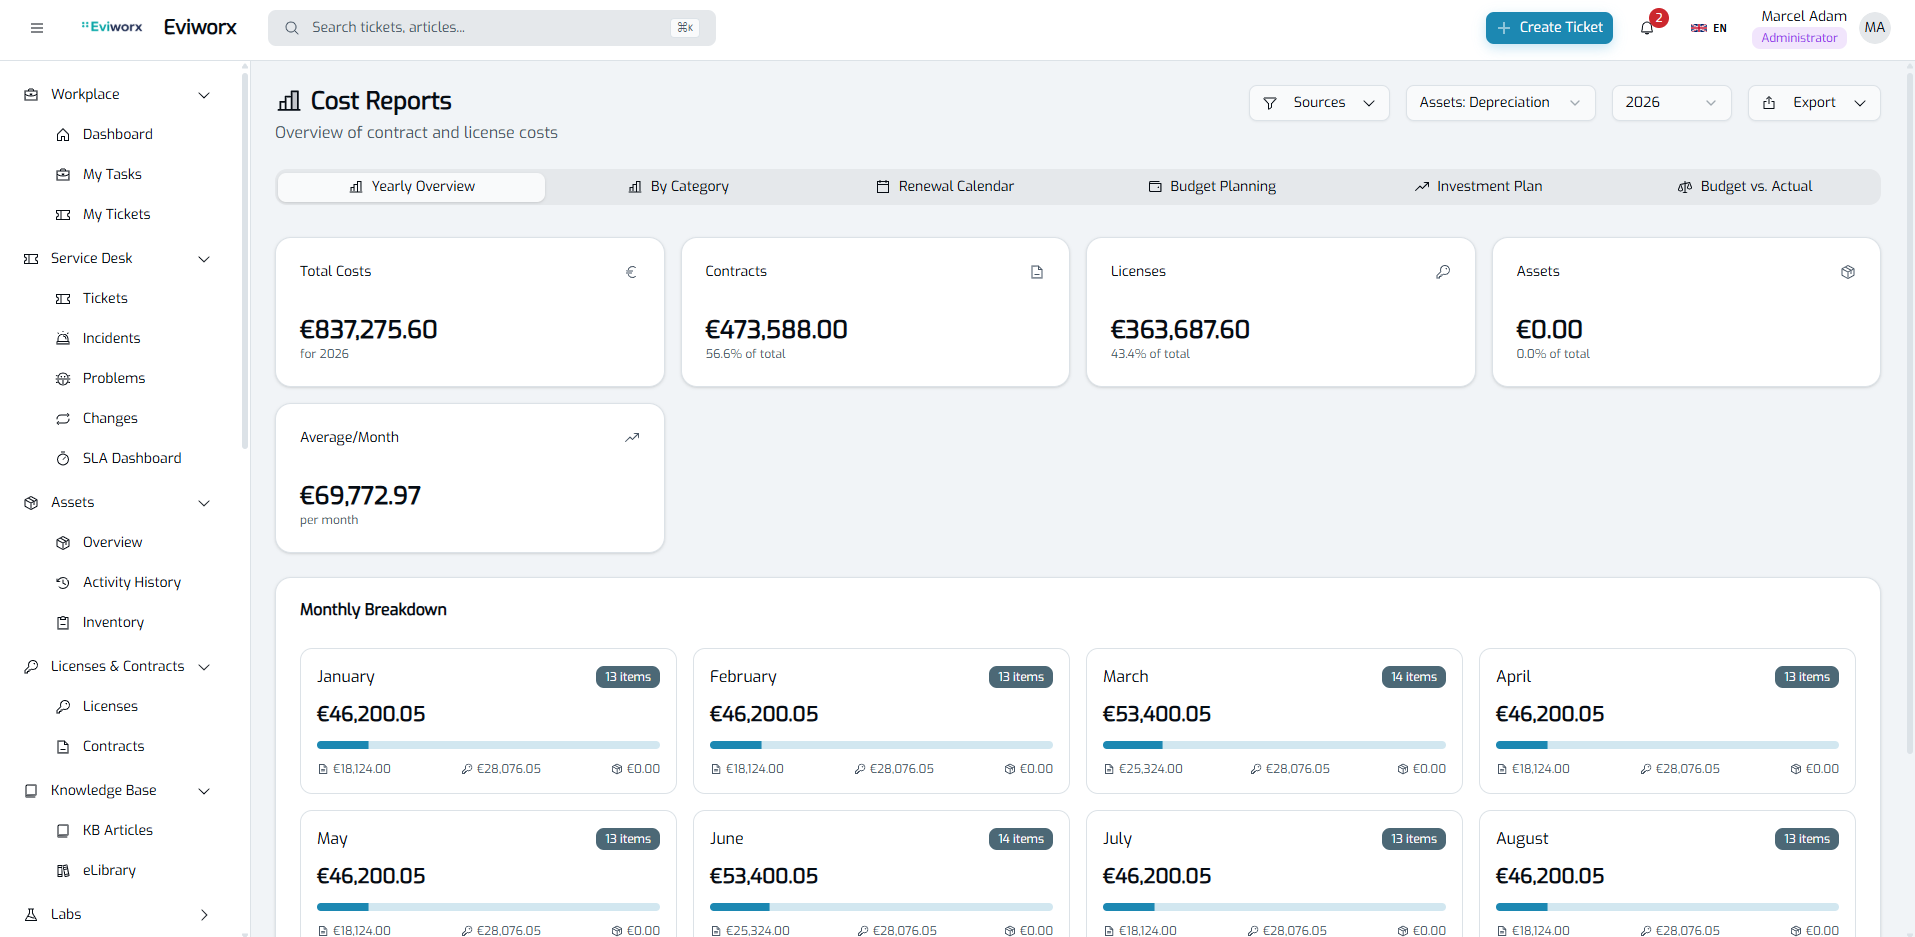
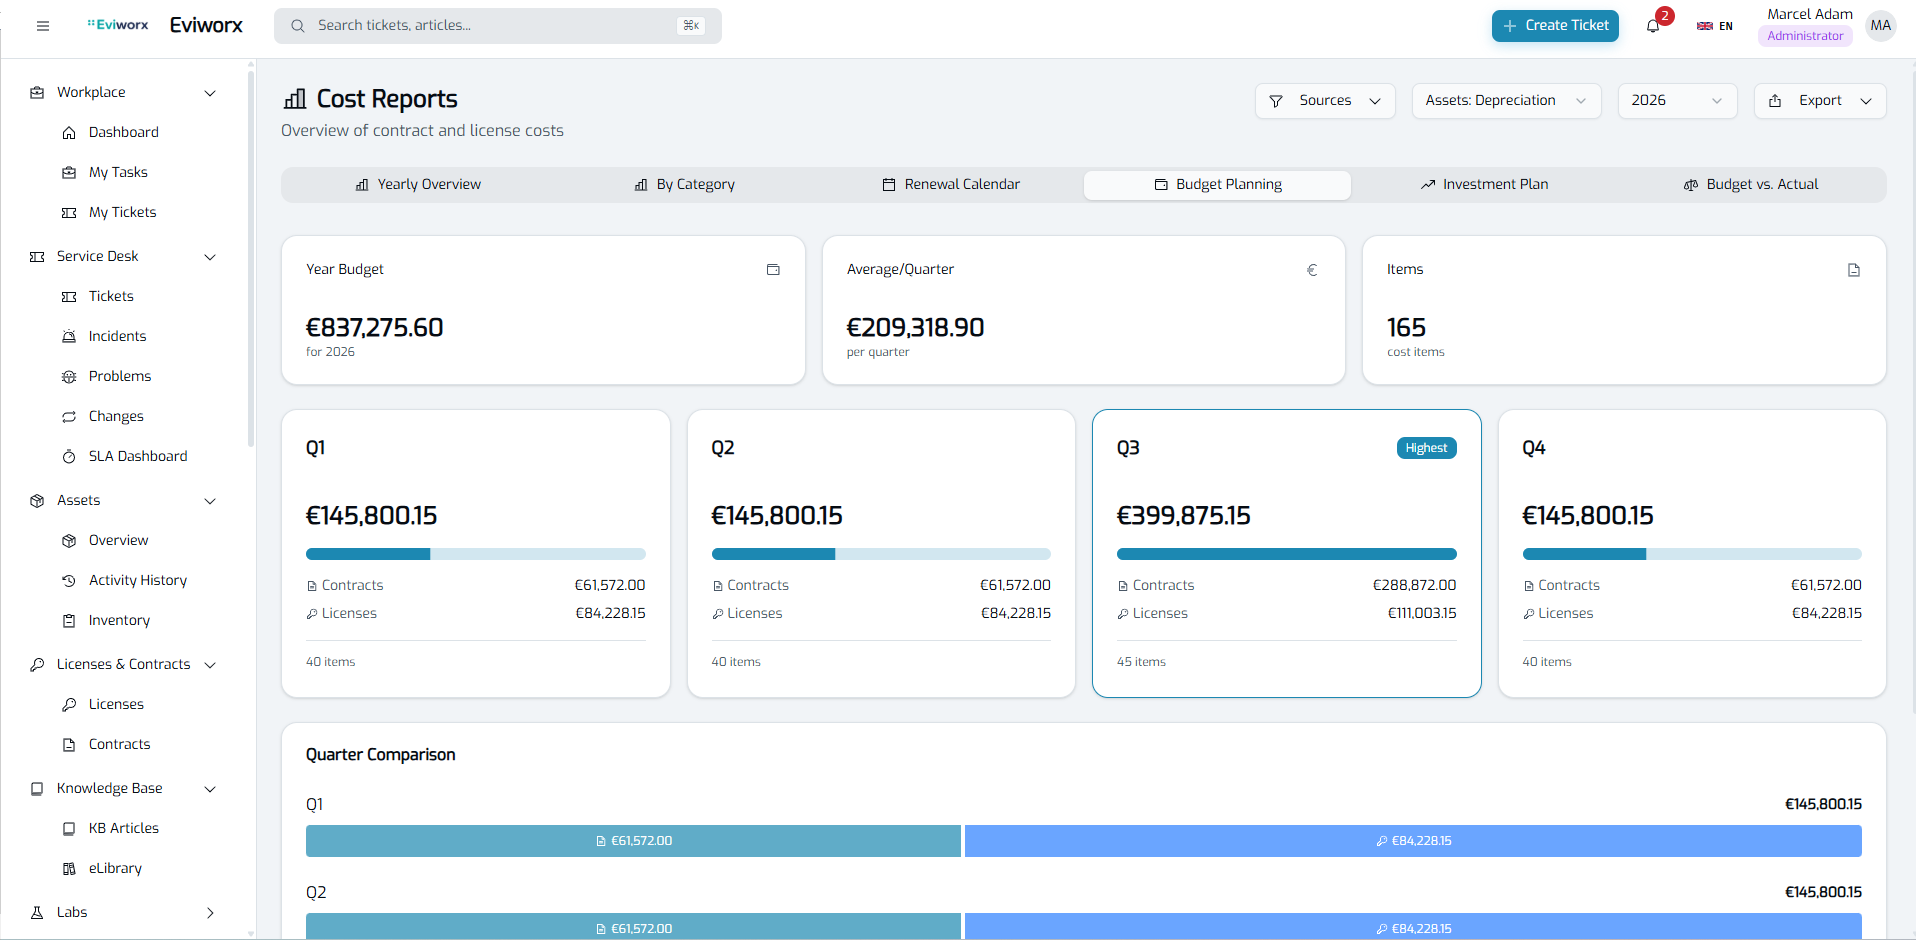
Costs & Budget, Transparent
Contracts, licenses and assets in one cost overview — including budget planning and plan-vs-actual across the year.
See More
Knowledge base, contracts, licenses, automation, reporting, architecture and more — the full product tour with every screenshot.
Who Is Eviworx For?
IT departments with roughly 5–100 agents.
Healthcare, manufacturing, energy, public sector.
Full control over data and infrastructure.
Security & Compliance
Security is not an add-on at Eviworx but an architectural principle.
- ✓MFA / TOTP
- ✓Entra ID SSO
- ✓Role model (RBAC)
- ✓Visibility scoping
- ✓100 % on-premise
- ✓Zero-trust virus scan
- ✓Encryption of sensitive data
- ✓Container hardening
- ✓SHA-256 chained audit history
- ✓GDPR support
- ✓NIS2-oriented processes
- ✓SBOM on request
Note: Eviworx supports you with architecture and processes in meeting GDPR and NIS2 requirements. This does not constitute a certification or a legally binding declaration of conformity.
For Technical Decision-Makers
Container architecture, SHA-256 hash-chained audit trail, multi-instance operation with distributed locks, workflow engine, SLA monitoring, lifecycle governance and a documented REST API — the technical details in the whitepaper.
Pilot & Pricing
30-day free trial, evaluate together. Then an individual licensing model fitting your size and operating model — one price, all modules included, billed by active agents.
Resources
Frequently Asked Questions
Answered briefly — details in the full FAQ.
Is Eviworx on-premise or cloud? +
Self-hosted in your own infrastructure — no SaaS, no third-party clouds. Your data stays with you.
How is it billed? +
By active agents (staff who work on tickets). End users, tickets, assets & all modules are unlimited and included.
Can I export my data? +
Yes, fully — CSV/JSON/PDF, direct PostgreSQL access and REST API. No vendor lock-in.
Does Eviworx support GDPR & NIS2? +
Yes, through architecture & processes — but without a certification or declaration of conformity.
Get in Touch
Tell us briefly about your requirements – we’ll get back to you promptly, happy to include an initial, no-obligation assessment.